Security Data Pipeline: Left-Shift Data Engineering
 Raju Chekuri: 24/09/2026
Digital Pulse: A Book by our CEO
Platform
Featured Videos
Digital Pulse: A Book by our CEO
Digital Pulse: A Book by our CEO
Published on September 24, 2026 | Last updated on September 24, 2026 | 2 min read
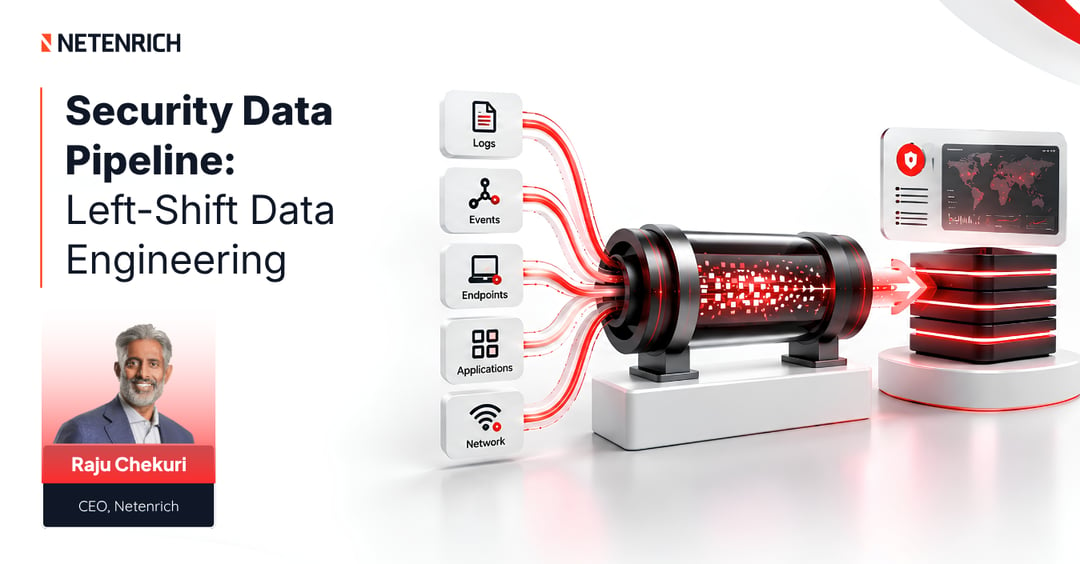
A security data pipeline is the architectural backbone that ingests, parses, enriches, and routes telemetry from enterprise environments to detection engines. However, a specific causal chain in how the SIEM-to-SOAR evolution unfolded that is worth naming precisely, because it reveals exactly why the fix has to happen upstream.
Classic SIEMs needed detection rules to identify threats in aggregated log data. Security teams wrote rules. As environments grew and telemetry volumes increased, the number of rules required to maintain coverage grew with them. Thousands of rules became the norm in mature environments. Each rule generated alerts. Many alerts were false positives - detections that matched the rule pattern but did not represent a real threat.
Alert fatigue followed. Analysts spending the majority of their time processing alerts that turned out to be benign. SOAR emerged to address this: automate the handling of routine alerts, orchestrate the workflow, free analyst capacity for real investigations.
But notice what SOAR addresses: the management of alerts that should not have been generated. The false positive problem is still there. SOAR makes it more efficient to process. The root cause — detection logic operating on raw, unenriched, inconsistently normalized data — is not addressed.
| Architectural Vector | Legacy SIEM-to-SOAR Pipeline | Left-Shifted Security Data Pipeline |
| Data Processing Point | Query-time translation and post-alert enrichment. | Native normalization and enrichment at the point of ingestion. |
| Detection Rule Focus | Bloated rules compensating for raw, inconsistent field formats. | Streamlined rules evaluating high-fidelity, contextualized telemetry. |
| Noise Reduction Method | Post-processing filters and automated SOAR closing scripts. | Upstream pre-filtering via statistical anomaly and sequence modeling. |
| Downstream AI & SOAR Efficacy | High risk of LLM hallucination and brittle SOAR execution. | Grounding for autonomous AI agents and deterministic SOAR playbooks. |
When telemetry is normalized at ingestion into a unified data model, cross-source correlation does not require translation logic. Rules can focus on detection logic rather than data quality compensation. The rule library shrinks as signal quality improves.
When events are enriched at ingestion with asset criticality, identity context, behavioral baseline deviation scores, and threat intelligence verdicts, the detection layer receives decision-relevant context automatically. False positives that exist because context was unavailable at detection time are eliminated.
When signal extraction - statistical anomaly scoring, behavioral deviation flagging, sequence pattern identification - runs on the enriched event stream before rules, the population of events that requires rule evaluation is pre-filtered. Rules operate on a higher-signal, lower-volume input and produce proportionally higher-quality outputs.
The downstream effects of an engineered security data pipeline compound across every operational layer:
The entire security architecture functions exponentially better when the foundation is right.
Fix the security data pipeline first. The rest follows.
Ready to eliminate alert fatigue and break the SIEM-to-SOAR noise cycle at the source? Fast-track your security operations with Netenrich to deploy a left-shifted security data pipeline and an AI-driven, Agentic SOC.
*Part of my ongoing series on data science and the future of security operations.*
The best source of information for Agentic SOC and Cyber Risk Operations best practices. Join us.