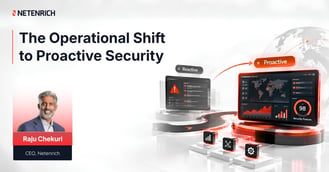
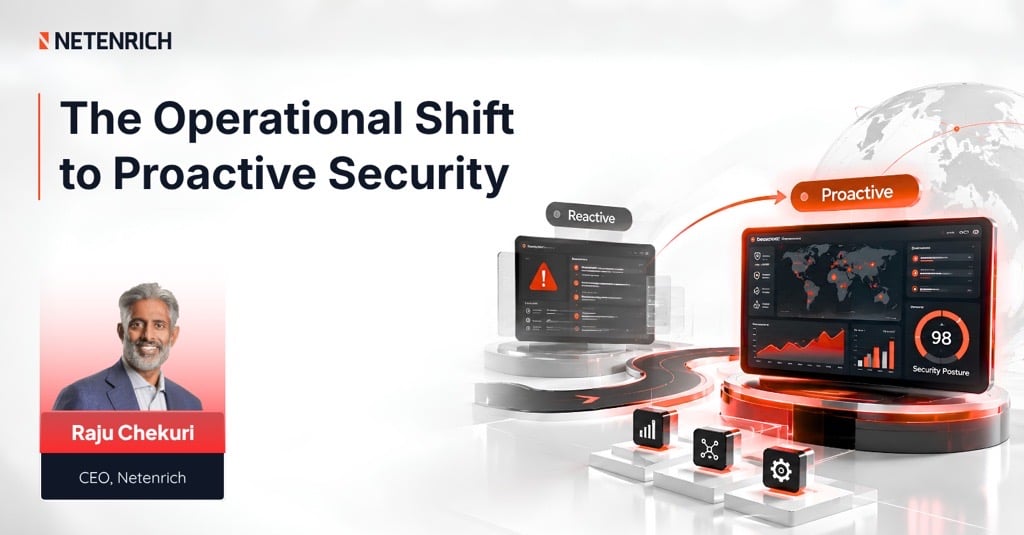
The Operational Shift to Proactive Security
 Raju Chekuri: 17/09/2026
Digital Pulse: A Book by our CEO
Platform
Featured Videos
Digital Pulse: A Book by our CEO
Digital Pulse: A Book by our CEO
Published on September 17, 2026 | Last updated on September 17, 2026 | 2 min read
The Resolution Intelligence Cloud was named deliberately. Not Detection Cloud. Not Response Cloud. Resolution Intelligence - the combination of intelligence that anticipates and resolution that closes the gap between what is and what should be.
This naming reflects the operational philosophy I want to describe in this post: the shift from incident-centric to intelligence-centric security operations.
Incident-centric operations is the dominant model. An alert fires. An analyst investigates. A determination is made. A response is executed. A ticket is closed. The incident is the fundamental unit of organizational work. Everything - capacity allocation, priority setting, success metrics, team incentives - flows toward and from incidents.
Intelligence-centric operations is organized around a different question. Not "what happened and what do we do about it?" but "what do we currently understand about the threat landscape relevant to this enterprise, and what does that understanding tell us to be looking for right now?"
| Operational Dimension | Reactive Incident-Centric SOC | Proactive Security Operations |
| Operational Trigger | Reactive alert generation from static SIEM rules. | Active threat intelligence feeds and real-time adversary models. |
| Analyst Capacity | 100% consumed by alert queues and manual ticket processing. | Protected capacity dedicated to hypothesis-driven threat hunting. |
| Detection Roadmap | Updated reactively after post-incident breach reviews. | Prioritized dynamically by evaluating MITRE ATT&CK coverage gaps. |
| Data Architecture | Siloed log storage with query-time translation delays. | Unified UDM security data lakes with real-time enrichment. |
Executing a successful shift to proactive security changes daily workflows across three critical vectors:
In proactive security operations, the hunting calendar is driven by the current threat model. When threat intelligence indicates elevated risk from a specific adversary technique targeting organizations in your industry, analyst capacity shifts toward looking for that technique proactively - regardless of whether detection has fired. The intelligence drives the operational agenda, not the alert queue.
Detection investment priorities are driven by coverage gaps against the threat model. When the threat model shows that a high-probability adversary technique has inadequate detection coverage, closing that gap is a priority - not because an incident occurred, but because the intelligence says the risk is real.
Analyst attention is updated by new intelligence in real time. When a new threat report arrives describing techniques relevant to the customer's industry, that intelligence immediately surfaces to the analysts working that environment as operational context - not in the next scheduled threat briefing.
The transition from incident-centric to intelligence-centric is both architectural and cultural, and both have to change together.
At Netenrich, intelligence-centric proactive security is the operational model we are working toward with every customer and building toward ourselves. The direction is clear. The investment required is real. The outcomes justify it.
Ready to move past reactive alert queues and shift to intelligence-driven defense? By deploying a Netenrich Agentic SOC to automate your routine incident triage, you can finally reclaim the protected analyst capacity required to hunt advanced threats proactively.
*Part of my ongoing series on data science and the future of security operations.*
The best source of information for Agentic SOC and Cyber Risk Operations best practices. Join us.