STAY AHEAD
Of the Adversary.
Always.
Assumed coverage is a guess dressed up as confidence. Provable Readiness replaces it with a number you and your board can actually trust.
The World's Most Sophisticated, Data-Driven Security Leaders Count on Us
THREE PILLARS
See it. Prove it. Then let it run itself.
Find what's actually exposed, prove the risk your other tools can't see, and let response move without waiting on a queue.
PROVABLE READINESS
Owning the tools was never the same as proving they work.
WHAT WE UNCOVERED
An AWS environment normally carried about 50 public facing assets. Over one weekend, that number drifted to 80. Nobody had approved the change, and nothing had alerted on it, because drift isn't a rule violation until someone is looking for it.
TO PROVE IT
We track posture drift continuously, so a quiet architectural change gets flagged before an attacker finds it first.
A team's MITRE coverage matrix showed detection rules mapped against credential-dumping techniques. When they ran a live test against that exact technique, the rule never fired. The log source it depended on had silently stopped parsing months earlier.
TO PROVE IT
We measure what's actually been proven, not what's claimed, and give you the real number.
One unpatched VPN opened the door to five separate threat-actor clusters, including espionage and two ransomware families. Nobody targeted this organization specifically. They targeted a vulnerability and took whoever was behind it.
TO PROVE IT
We find the exposed entry points before they're found for you.
One team's EDR dashboard showed green across the board. The underlying telemetry told a different story: it was silently failing to catch identity-based lateral movement, the exact technique their top threat relies on.
TO PROVE IT
We validate that a control is actually firing, not just installed.
A vulnerability backlog was prioritized by severity score alone. Once it was mapped against how active threat actors actually chain their techniques together, the order flipped: a lower-scored exposure with live exploit activity outranked a higher-scored one nobody was using.
TO PROVE IT
We prioritize by threat-informed detection, not a static score, and keep that model current as new actors and techniques emerge.
A QUESTION THIS ANSWERS
"Can we prove our defenses will hold, or are we just hoping they do?"
Proof Over Assumption
UNCOVER INVISIBLE RISK
Stop assuming your cloud is secure. Prove it against the threats that actually matter.
WHAT WE UNCOVERED
A CISO believed their AWS environment was locked down. A legacy CI/CD vendor still held a dormant, over-permissioned IAM role, a non-human identity with a live path straight into production databases.
TO DETECT IT
We map every non-human identity, service account, and API key, so a dormant one can't become someone else's way in.
When the Shai-Hulud attack compromised 180+ NPM packages, every rule-based tool watching saw a normal software update. None of them were built to question a signature they were designed to trust.
TO DETECT IT
We flag the trust relationships attackers exploit, not just the signatures they evade.
A massive data download fired at 2am. To the SIEM, it looked identical to a routine deployment, the kind of ambiguity that takes a human hours to resolve, if anyone's watching at 2am at all.
TO DETECT IT
We tell the difference between a routine deployment and an active exfiltration before it matters.
An extortion crew called an employee's personal mobile posing as IT helpdesk, intercepted their MFA code at a spoofed portal, then deleted the alert emails behind them. The MITRE heatmap still showed identity as green.
TO DETECT IT
We surface identity attacks that never trip a technical alert.
An innovation team deployed a self-hosted LLM on cloud compute to analyze customer data, bypassing the standard architecture review. To the tools watching, it looked like normal compute traffic. Nobody flagged it until someone went looking for exactly this kind of workload.
TO DETECT IT
We recognize the behavioral signature of an AI workload touching sensitive data, so shadow AI doesn't get to hide as routine compute.
A QUESTION THIS ANSWERS
"Which identity-based backdoors are active right now that our tools are built to ignore?"
Nothing Stays Hidden
AUTONOMOUS SECURITY OPERATIONS
You bought the SIEM, the SOAR, the MDR. None of them fixed how long triage actually takes.
WHAT WE UNCOVERED
A state sponsored group used an agentic AI tool to infiltrate roughly 30 organizations. The AI ran reconnaissance, found vulnerabilities, wrote exploit code, harvested credentials, and moved laterally on its own. A human only stepped in at four to six decision points across the entire operation.
TO PREVENT IT
Most security teams and tools are built to catch human-speed attacks. We built ours to catch the machine-speed ones too.
An analyst starts their shift already behind, with a queue built up overnight and more identities and integrations added since yesterday. By the time the real one gets triaged, the attacker has already moved laterally.
TO PREVENT IT
We triage by business impact first, so the real one doesn't wait behind the noise.
A team is three years into a SIEM contract signed for a slower era, built for threats that gave them hours to respond. Their newest adversary finishes its objective in minutes.
TO PREVENT IT
We close the loop at machine speed.
One vulnerability's exploitation activity spiked more than 100x in a single week while thirty other threat clusters quietly faded. The team's risk assessment, written two months earlier, didn't mention it at all.
TO PREVENT IT
We track what's accelerating right now, not what was true when the report was written.
A QUESTION THIS ANSWERS
"How do we stop bringing a human team to a machine-speed fight?"
Built to Keep Pace
The Shift from Efficiency to Efficacy
Security must become a data game.
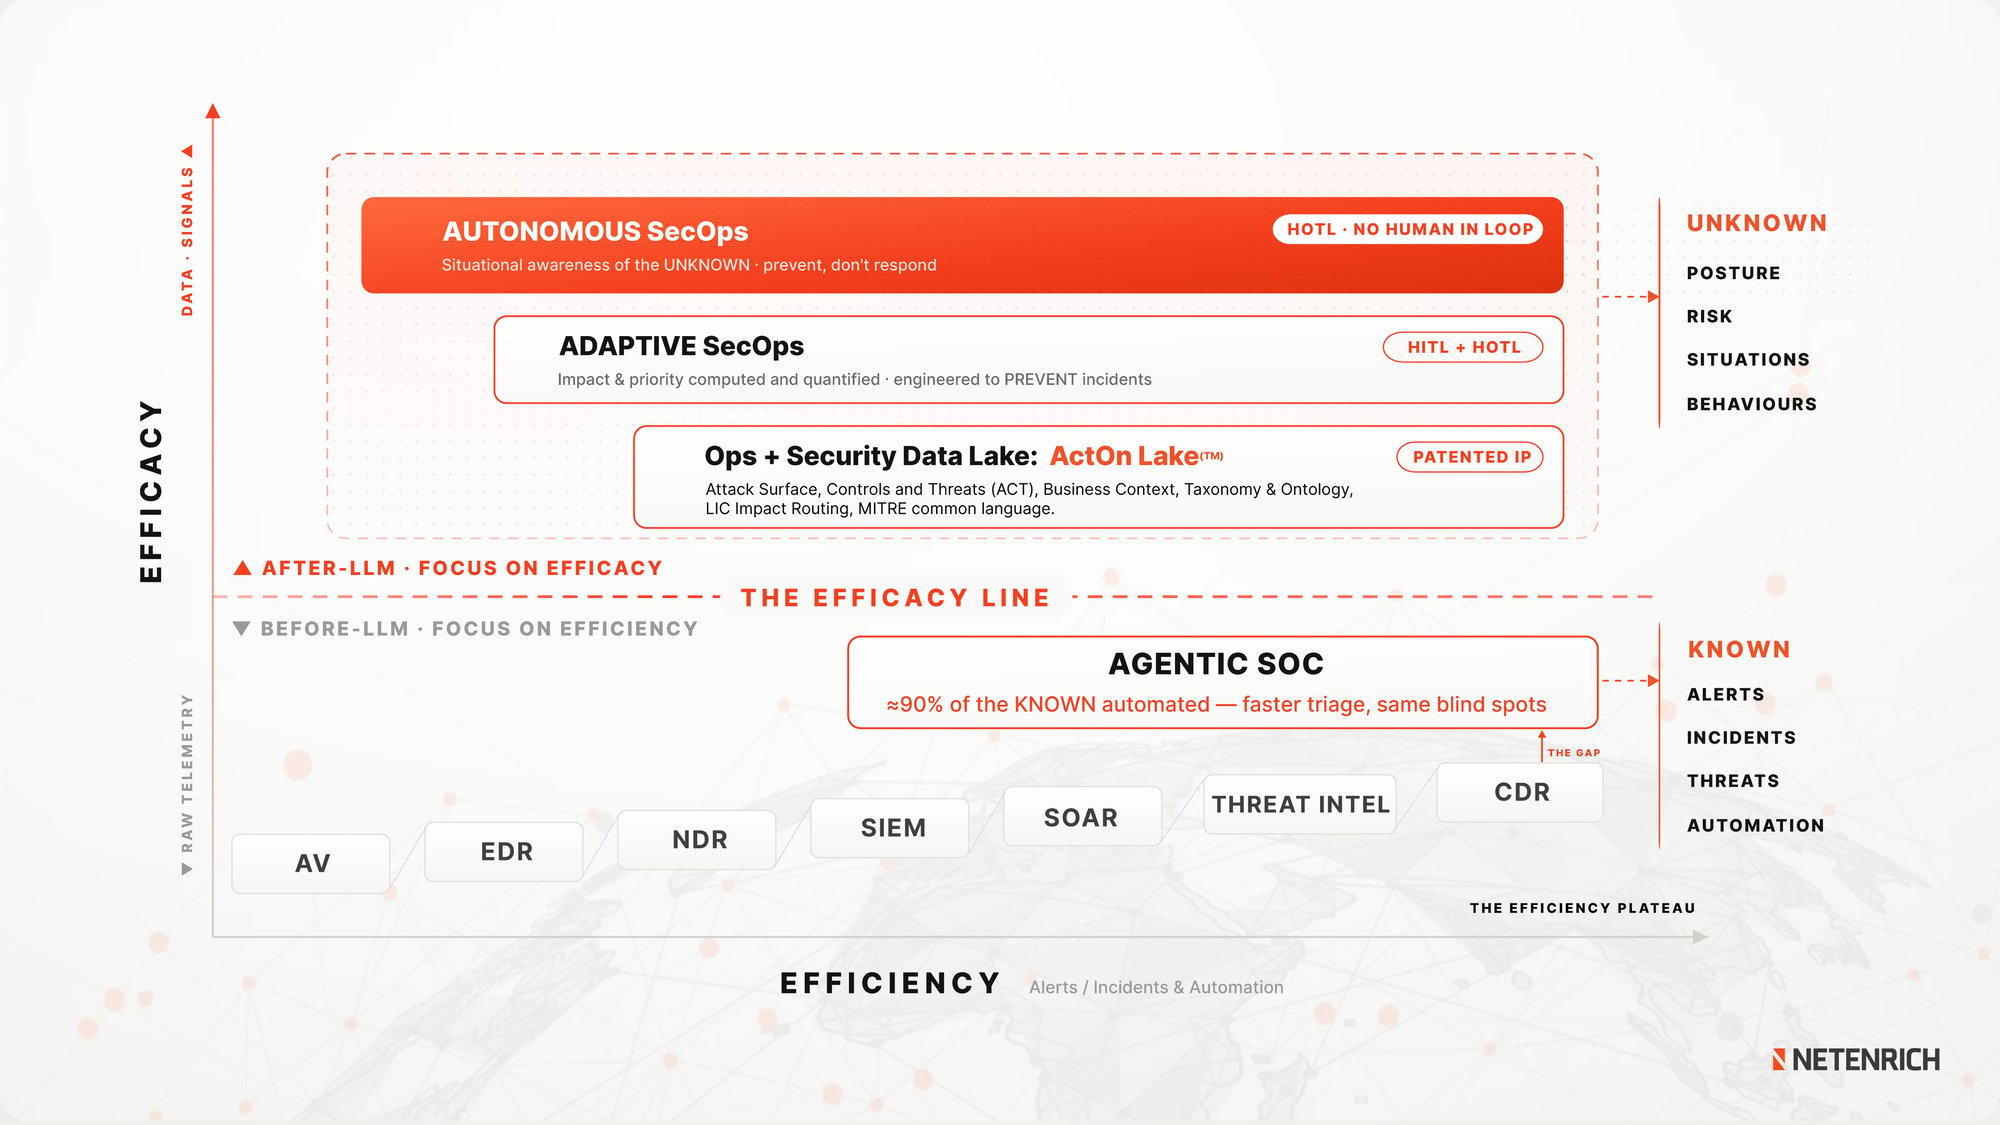
Same platform lesson. Security must become a data game.
Recently, Netenrich CEO, Raju Chekuri, spoke to an onboarding class for new Netenrich employees on our approach to Autonomous Security Operations and walking through. View that video here.
Cruise control is not self‑driving.
Diesel & Petrol
Decades perfecting combustion.
Manual → Automatic
Without this shift, cruise control never happens.
Cruise Control
Then progress stalled for ~40 years.
Electric + Software
The fundamental platform shift.
Full Self‑Driving
Autonomy became possible.
AV · EDR · NDR
Signature era.
SIEM · SOAR
Automate the playbooks.
MDR · Agentic SOC
Faster triage, same blindness.
Adaptive SecOps
Data-Driven: ACT · LIC · ActOn Lake · ActOns.
Autonomous SecOps
Prevent, not just respond.
Same platform lesson. Security MUST become a data game.
The adversary already crossed the line.
First large‑scale AI‑orchestrated cyberattack
A state‑sponsored group used an agentic AI tool to infiltrate ~30 global targets. AI executed 80–90% of the operation autonomously — recon, vulnerability discovery, exploit code, credential harvesting, lateral movement, exfiltration. Humans intervened at only 4–6 decision points per campaign.
AI finds what decades of tools missed
An AI model autonomously discovered 10,000+ high‑severity vulnerabilities across 1,000+ open‑source projects — including a 17‑year‑old FreeBSD RCE and a 27‑year‑old OpenBSD flaw. Mozilla fixed 271 Firefox vulnerabilities in two weeks. These are infrastructure vulnerabilities — not CISO problems alone.
of organizations hit by AI‑enabled attacks in 2025
YoY increase in AI‑powered cyberattacks
of phishing emails contain AI‑generated content
of Glasswing‑discovered vulnerabilities unpatched
These threats cut across the CTO, CIO, and CISO — infrastructure, software supply chain, cloud, identity, and endpoints. Security is no longer one office's problem.
The barriers to sophisticated cyberattacks have dropped substantially — and they will continue to do so.
Sources cited on page: Anthropic Nov 2025 & May 2026 · MITRE ATT&CK C0062 · Cybersecurity Dive · Google GTIG Nov 2025 · The Hacker News May 2026 · AISI UK Apr 2026. Flagged on the live page as needing re‑verification before publishing.
Stop the adversary before they ever get in.
You can keep assuming your defenses hold — or you can prove it, with a Provable Readiness score built from your own environment, not a vendor's claim.
Delivering Real-world
Outcomes for Global Enterprises
Don’t take our word for it – hear directly from our customers about how we transformed their security operations.
“Netenrich gave us clarity we didn’t have before. By collapsing dozens of disconnected workflows into a small number of risk-driven operating paths and materially expanding our detection coverage, we moved from managing alerts to managing risk. We now operate with far greater confidence and precision.”
Kumar Palaniappan
CISO, Citrix (Cloud Software Group)
“With Netenrich and Google SecOps, our team focuses on what actually matters — meaningful investigations and risk decisions, not chasing noise. We can now explain our security posture clearly to leadership and show how our controls, detections, and response align to business risk.”
Harsh Jha
CTO, Nuvama Group
“Netenrich didn’t just solve today’s problems. They helped us adopt an operating model that scales as our environment changes. Our security operations are now adaptive, resilient, and built for long-term risk management.”
CISO
Healthcare Organization

