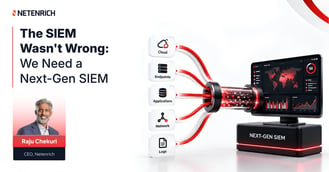
The SIEM Wasn't Wrong: We Need a Next-Gen SIEM
 Raju Chekuri: 22/09/2026
Digital Pulse: A Book by our CEO
Platform
Featured Videos
Digital Pulse: A Book by our CEO
Digital Pulse: A Book by our CEO
Published on September 22, 2026 | Last updated on September 22, 2026 | 2 min read
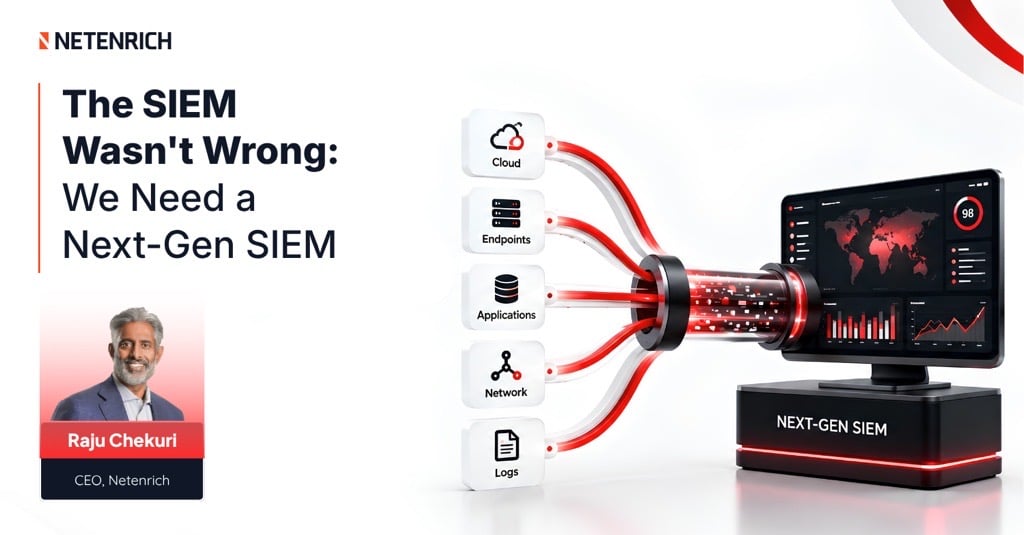
I want to be honest about something that gets lost in conversations about the future of security operations: the past was not wrong.
SIEMs solved a genuine problem. Before centralized log management, security events from different systems lived in separate log files with no mechanism for cross-system correlation. SIEM created a central repository, a query interface, and a framework for rule-based detection that gave security teams a unified visibility layer for the first time. For the telemetry volumes and correlation requirements of the era they were designed for, this was meaningful progress.
SOAR solved a different genuine problem. The manual workflow overhead of security operations - alert received, look up context, check threat intelligence, create ticket, notify team, run containment procedure - was consuming analyst time at a rate that was not sustainable. SOAR automation removed human steps from well-defined, repetitive workflows. That was real efficiency.
Threat hunting as a practice solved the detection gap problem. When rules and correlation cannot catch everything, skilled humans looking proactively for adversary presence not yet surfaced by detection logic adds coverage that no automated system provides. The development of threat hunting as a discipline was genuine progress.
The problem is not that these things were built. The problem is that the architecture underlying them - designed for the telemetry volumes, correlation requirements, and adversary sophistication of their era - cannot scale to where we are now.
| Capability Vector | Traditional Legacy SIEM & SOAR | Modern Next-Gen SIEM Architecture |
| Data Ingestion | Schema-less log dumping or rigid query-time parsing. | Native normalization into canonical UDM security data lakes. |
| Detection Logic | Static, threshold-based correlation rules. | Dynamic behavioral baselining, sequence modeling, and ML inference. |
| Workflow Automation | Brittle IF-THEN SOAR scripts that break on edge cases. | Goal-oriented Agentic SOC workflows with strict governance guardrails. |
| Investigative Speed | Slow batch queries running over hours or days. | Sub-second retroactive search across petabyte-scale telemetry. |
Modern enterprise environments generate orders of magnitude more security-relevant telemetry than traditional SIEM architectures were designed to process.
The operational breakdowns in legacy architectures stem from three main limitations:
The right response to this is not to disparage what was built. It is to acknowledge the limits, understand what the next layer requires, and build it deliberately - on a foundation informed by everything that worked and designed to address what could not scale.
That is the intellectual stance behind the Resolution Intelligence Cloud. Deep respect for the foundation the industry built. Clear-eyed acknowledgment of its limits. And a specific, grounded vision for what comes next - built on data science principles, trained on the domain knowledge accumulated through years of building on that foundation.
The past created the knowledge base for the future. The future requires building differently.
Ready to move past legacy SIEM bottlenecks, expensive log ingestion fees, and rigid SOAR playbooks? Fast-track your security operations with Netenrich to deploy an AI-driven Agentic SOC.
*Part of my ongoing series on data science and the future of security operations.*
The best source of information for Agentic SOC and Cyber Risk Operations best practices. Join us.