Probabilistic Security & Attack Path Management
 Raju Chekuri: 15/10/2026
Digital Pulse: A Book by our CEO
Platform
Featured Videos
Digital Pulse: A Book by our CEO
Digital Pulse: A Book by our CEO
Published on October 15, 2026 | Last updated on October 15, 2026 | 2 min read
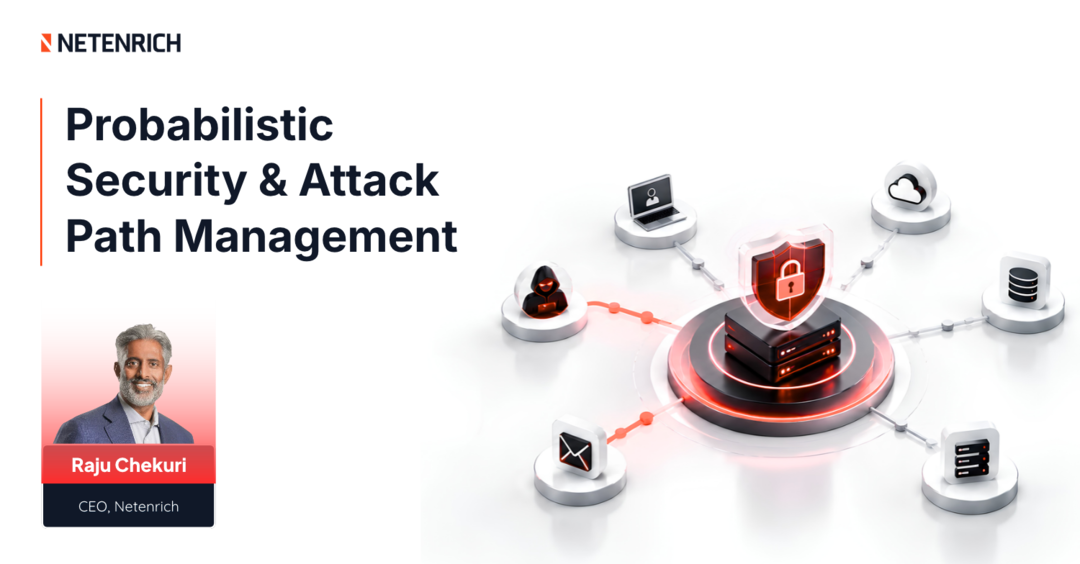
Adversary path modeling is the capability that most directly embodies probabilistic security thinking - the practice of understanding, before any adversary activity begins, which paths through your environment an adversary would most rationally pursue.
The conceptual foundation is straightforward. Adversaries who have achieved initial access move through environments using the access relationships that already exist. They traverse the topology - from compromised account to accessible system, from that system to harvestable credentials, from those credentials to new systems - following paths created by legitimate operational requirements. Every path they can take exists because someone needed it to exist for a business reason.
This means the adversary's lateral movement roadmap is already in your environment, encoded in the access graph. The question is not whether those paths exist - they do. The question is whether you have mapped them before the adversary does.
In the Resolution Intelligence CloudTM, adversary path modeling runs as a continuous analytical process against the evolving access topology of every customer environment.
We start from real-world exposure points:
From those starting nodes, our engine traverses the relationship graph. It maps which high-value targets are reachable, flags the intermediate systems acting as stepping stones, and tallies the exact hop count required to reach sensitive data.
The outputs serve several specific operational purposes.
The accounts and systems that provide an adversary with the broadest or most critical access if compromised are identifiable before any incident. These are the highest-priority hardening targets - the access concentrations where privilege reduction, stronger authentication, or additional monitoring has the highest security return.
The path traversal consistently surfaces access relationships with no current operational justification - project access never revoked, service account permissions that accumulated beyond their intended scope, inherited group memberships from deprecated roles. These are unintentional attack paths that can be closed before an adversary finds them.
The paths from common initial access points to critical targets are the ones a rational adversary would prioritize. Applying heightened detection sensitivity to activity along these specific paths - rather than broad alerting that generates noise - creates targeted coverage for the most probable adversary approaches.
The system updates continuously as the environment changes. New assets deployed, new access grants created, new vulnerabilities discovered - each changes the path topology and the model reflects it immediately.
The adversary is mapping your environment. The only question is whether you are mapping it first.
Tired of chasing reactive alerts after an attacker is already moving laterally? Partner with Netenrich to operationalize continuous attack path management, eliminate hidden choke points, and build a proactive Agentic SOC.
*Part of my ongoing series on data science and the future of security operations.*
The best source of information for Agentic SOC and Cyber Risk Operations best practices. Join us.