Would Your Stack Catch This Wire Transfer Heist, Or Just Watch It Happen?
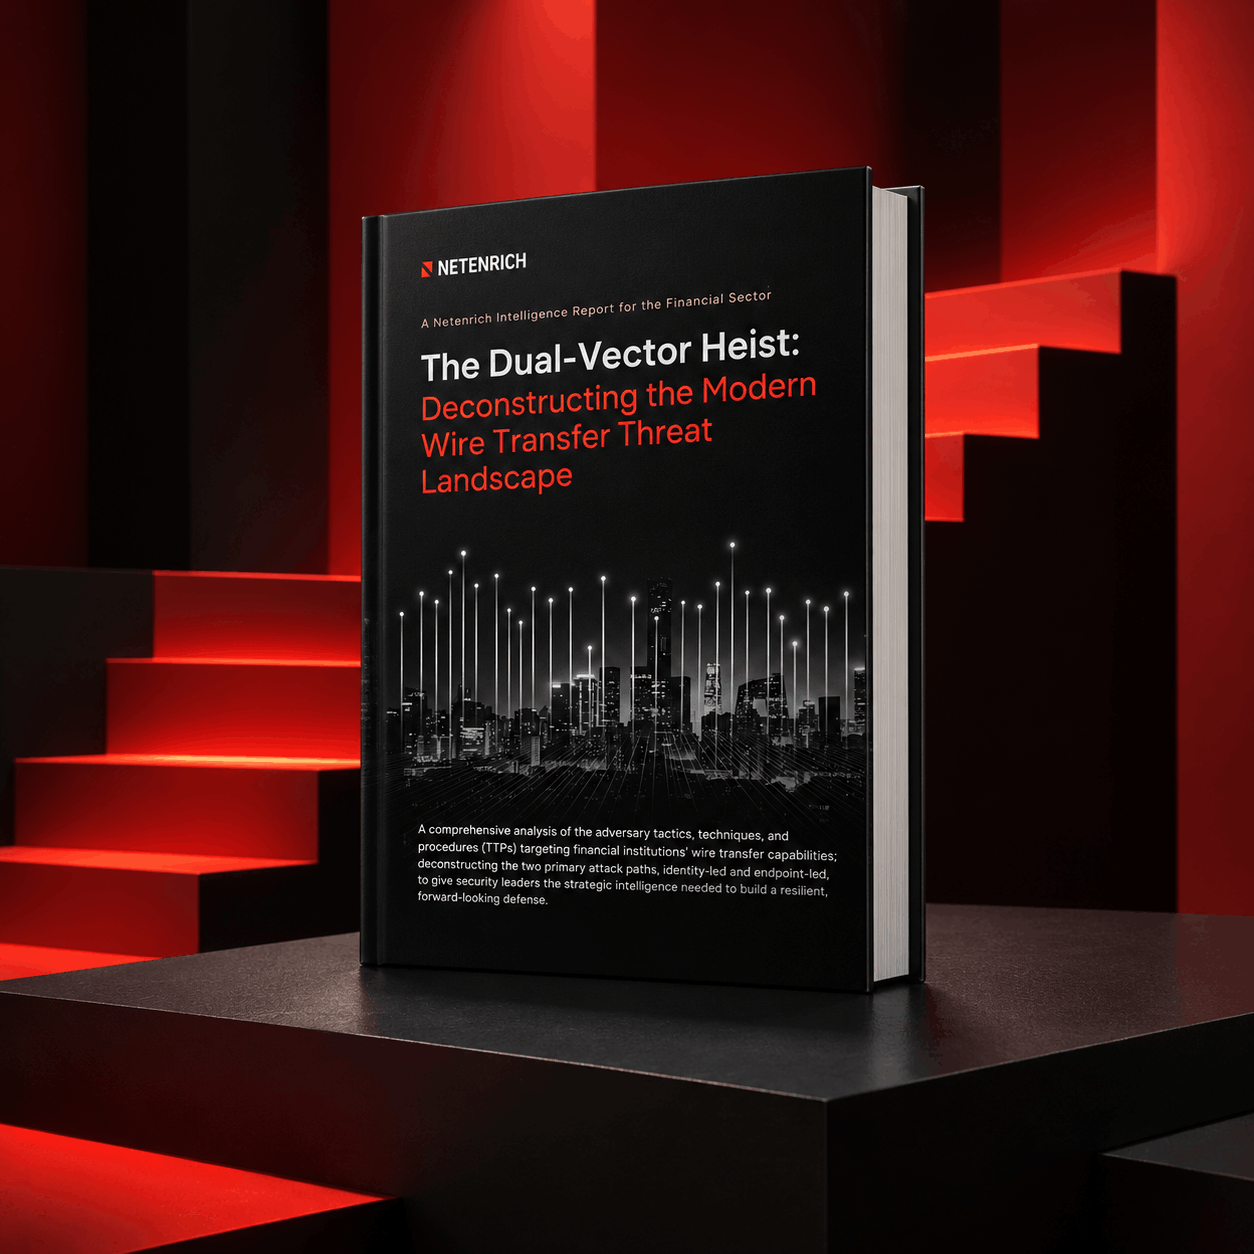
Inside The Dual-Vector Heist: how financially motivated groups are exploiting two distinct attack paths (identity takeover and endpoint compromise) to move money out the door before your team ever sees an alert.
Inside the report
Two Paths, One Objective
Wire transfer fraud has stopped looking like phishing. Today's attacks are patient, multi-phase operations, and nearly all of them succeed by running through one of two attack paths. Both are built to survive inside the controls you already have, long enough to move funds before anyone raises an alarm.
Track A: The Identity Heist
Discover how attackers hijack user identities, bypassing MFA and conditional access to operate undetected from within.
Track B: The Endpoint Breach
Explore the methodology of compromising an endpoint to maneuver laterally and directly manipulate financial controls.
What You'll Uncover
This report breaks down exactly how both paths unfold, start to finish, and what it would actually take for your organization to see them coming instead of finding out after the wire has cleared.
How two attack paths, one identity-led and one endpoint-led, carry an attacker from first contact to fraudulent wire transfer, often before detection is even possible.
Which named, financially motivated threat groups are actively running this playbook against financial institutions today.
Why owning the right security tools isn't the same as being able to prove they'd catch this, and where that operational gap most often hides.
The one critical blind spot most financial institutions carry without realizing it, and the exact cost when an attacker finds it first.

